
instract Deployment
Deployment in our cloud, your cloud or your data center.
Forward deployed engineers install, configure and release each system under your security policy, with your keys and single sign-on.
Forward deployed engineers and deployment strategists
Each engagement has a named team that works at your site until the system is in production and your staff can operate it.
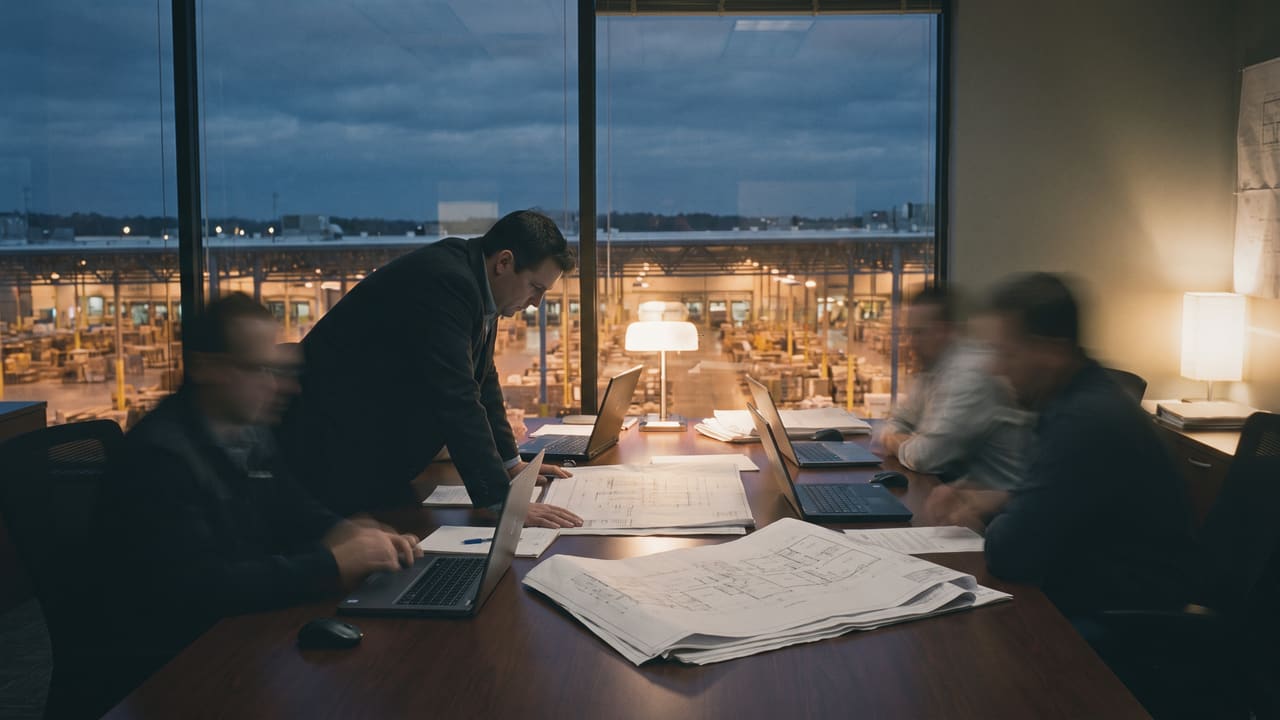
Forward deployed engineers
Build agents, integrations and controls in your environment, then release them to production.
- Works at your sites
- Access under your policy
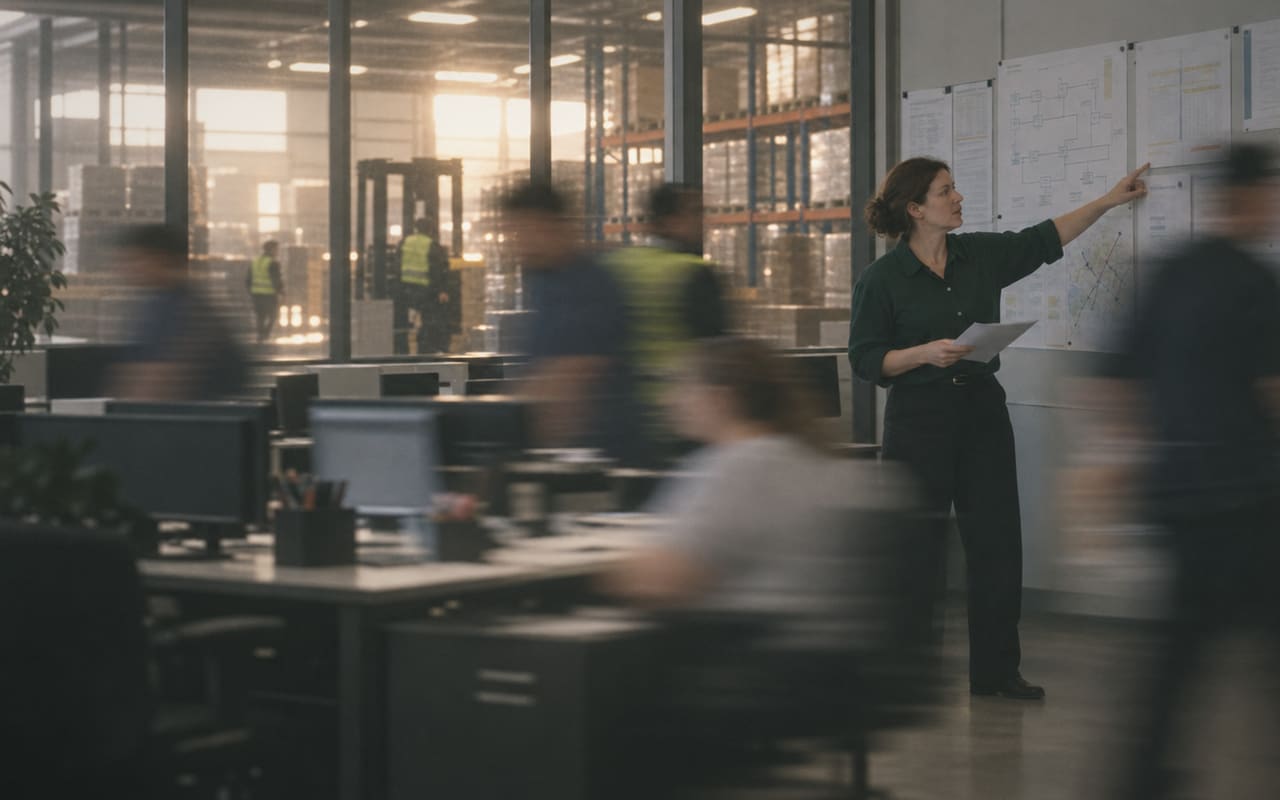
Deployment strategists
Document each process with its owners, agree success measures with your sponsor and report on them.
- Reports to your sponsor
- Weekly status report


Handover to your team in three phases
The handover schedule is set in the statement of work. Each phase closes when your team signs off.
Deploy
Our engineers build and release. Your team reviews and approves each change.
Operate together
Your team approves releases and runs daily operations. Our engineers support.
Client owned
Your team owns the roadmap and the releases. Support continues under contract.
Operated by Instract
Operated by your team
- Runbooks, architecture documents and admin access
- Change control, monitoring and on call
- Roadmap, budget and vendor decisions
Four deployment models
Every model runs the same software, release process and audit trail. They differ in who operates the infrastructure and who holds the keys.
Instract cloud
Hosted and operated by Instract in a logically isolated tenant, updated continuously.
Identity provider
Single sign-on, SAML or OIDCInstract cloud, us-east-1
Isolated tenant
The application
Instract managed keys
Fully managed
A dedicated environment for your organization, hosted and operated by Instract.
Identity provider
Single sign-on, SAML or OIDCDedicated network
Dedicated environment
The application
Customer managed keys available
Customer cloud
Installed in your cloud account and region, under your network and key policies.
Identity provider
Single sign-on, SAML or OIDCCustomer network
Customer cloud account
The application
Customer managed keys
On premises
Installed in your data center. Can run with no external network connection.
Identity provider
Single sign-on, SAML or OIDCCustomer site network
Customer data center
The application
Keys in your own HSM
One platform for how your business runs
Every part shares the same records, approvals and audit log, so each one you add works with the rest.
instract Strategy
Strategists on site, from the first map to production.
Explore Strategy
instract AI OS
One operating layer for people, agents and apps.
Explore AI OS
instract Agents
Governed agents that run work around the clock.
Explore Agents


